Whatever's asking for proof, a public sector tender demanding CAF alignment, an enterprise client's ISO 27001 vendor assessment, or an insurer tightening underwriting, one platform assesses your gaps, builds the required policies, risk register and evidence, and keeps you ready. Built from your real answers, kept current automatically.
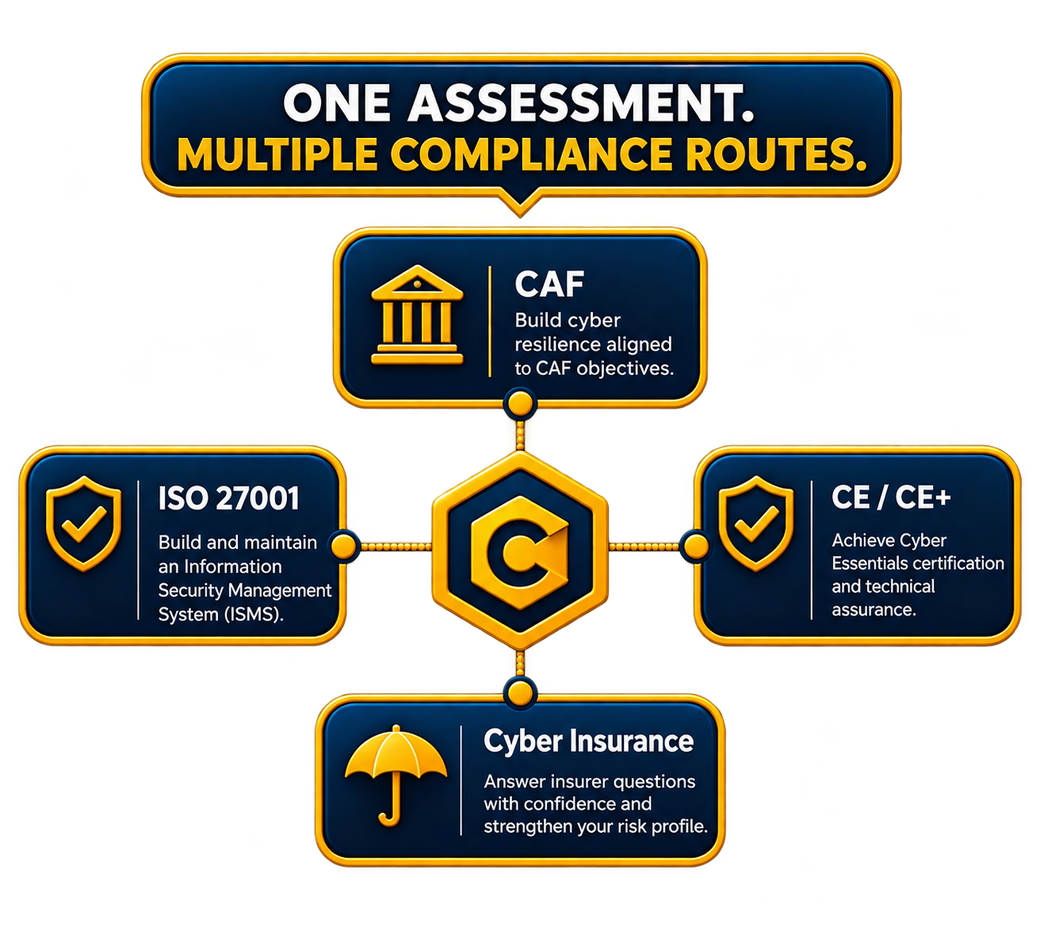
Answer once. Your answers map straight onto whichever route applies to you, CAF, ISO 27001, Cyber Essentials/CE+, or Cyber Insurance evidence, so you're never redoing the same work for a second framework.
Get ready for certification, tenders and cyber insurance, without needing to become a security expert first.
Add a compliance layer to your existing customer relationships, without building your own GRC service.
Give clients a structured cyber-readiness pathway ahead of placement or renewal.
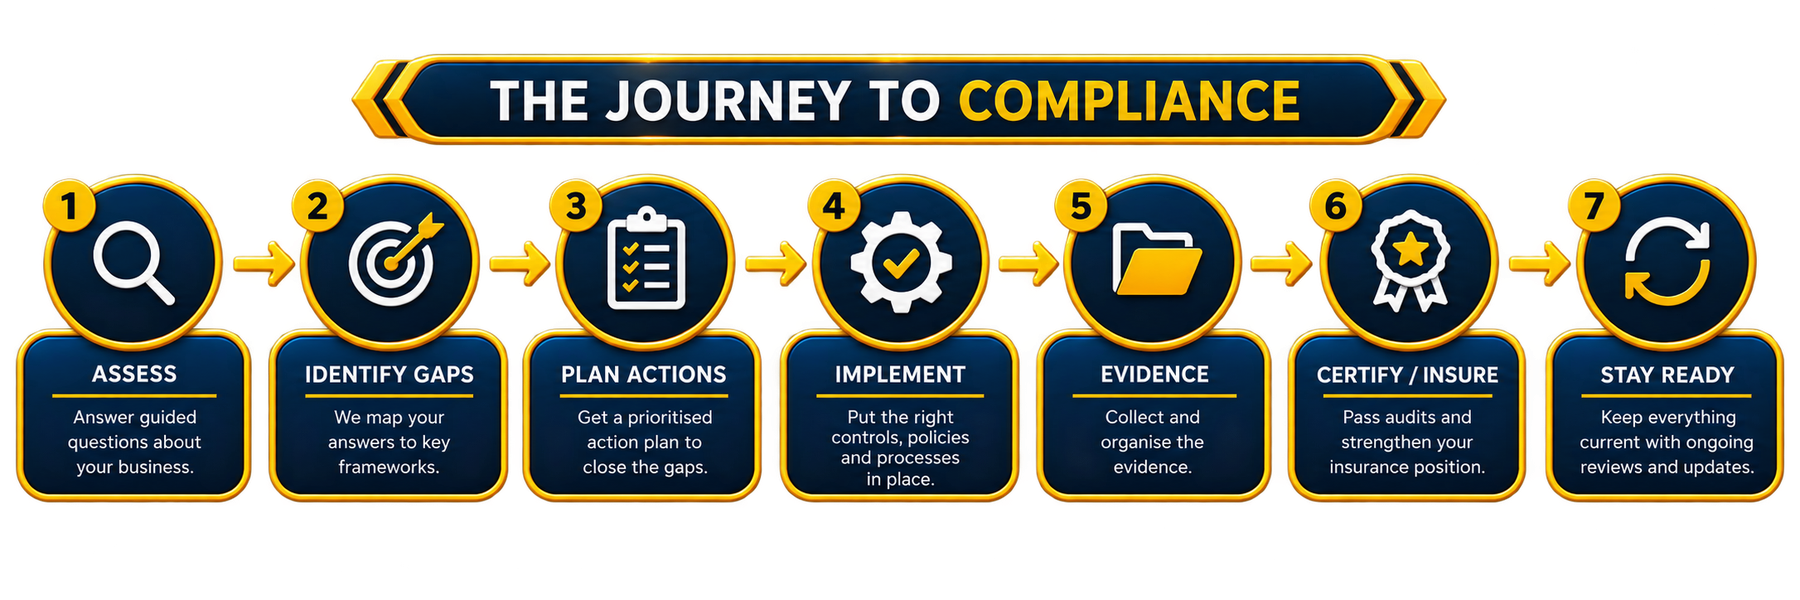
A customer, tender, or insurer is asking for proof of something, and you just need it handled. Answer our guided questions in plain English about how your business actually runs, no security background required, and we turn that into the audit-ready evidence they're asking for.
Every answer is mapped to the framework your package covers, CAF's Contributing Outcomes and your ISO/IEC 27001:2022 Statement of Applicability with the Cyber Assurance Policy Pack, or Cyber Essentials' technical controls with Cyber Essentials/CE+, reviewable, defensible, and kept current as your environment changes, not a one-off document dump.
We are seasoned Governance, Risk, and Compliance security consultants with decades of hands-on experience protecting critical infrastructure, spanning complex corporate business sectors and highly classified Government departments.
UK small businesses and local authorities face intense pressure to maintain robust documentation. Traditional consultancies charge fees you can't afford; downloadable templates are static, generic, and fail to match your real-world setup, leaving you functionally uninsurable or blocked from tenders.
To productise compliance consulting and remove the manual drafting bottleneck, closing the gap between cheap, useless templates and the high cost of traditional consultancy, without cutting the corners that make consultancy expensive in the first place.
We've spent years inside sensitive Government frameworks, directly designing and auditing systems to rigorous national security guidelines, and deploying compliance strategies across fast-scaling fintech and critical healthcare providers alike.
The Cyber Assurance Policy Pack (covering CAF, ISO 27001 and Cyber Insurance) or the lower-cost Cyber Essentials / Cyber Essentials Plus package, whichever matches what your procurement team, enterprise client or insurer is actually asking for.
Complete a secure, customised set of questionnaires scoped to your package, the full Cyber Assurance Question Pack, or the shorter CE+ question set, to automatically populate your framework-aligned policies.
Static documents fail over time. Update an answer and we flag every document it affects; automated review-reminder emails keep you on schedule too, so your evidence stays current, long after day one.
We have spent years inside sensitive Government frameworks, directly designing and auditing systems to meet rigorous national security guidelines. We know exactly how procurement teams evaluate risk, and we don't just read compliance checklists, we've spent decades implementing them, with an exhaustive operational understanding of the NCSC CAF, ISO 27001, Cyber Essentials, and UK NIS Regulations.
Traditional GRC consultants take weeks of back-and-forth meetings just to draft your baseline policies. Our automated engine generates your first policy draft instantly from your intake answers, then updates it automatically as you complete the rest of your guided questions.
We bridge the gap between slow, expensive compliance consultants and dangerous, public AI tools, delivering enterprise-grade security documentation tailored precisely to your business, without the corporate price tag.
From fast-scaling fintech platforms to critical healthcare providers, our consultants have deployed robust compliance strategies across highly regulated, risk-averse commercial environments, and inside Government itself.
Not a template farm, written by people who've sat on the other side of the audit.
Your data never leaves a UK server boundary, and never touches a public AI cloud.
Change an answer, regenerate the affected document, no stale policies gathering dust.
Mapped to real framework controls, not a generic document dump with your name swapped in.
Your questionnaire answers, policies, evidence and every generated document are processed and stored entirely inside our own UK server boundary, and never touch a public AI cloud. (Payment processing is handled separately by Stripe, see our Sub-Processors page.)
Self-hosted on our own UK server boundary, not a US-owned cloud broker.
Every generated document is AES-256 encrypted the moment it's created.
Pre-vetted, expert-authored policy libraries, not a language model writing from scratch.
Cancel and your documents and questionnaire answers are automatically purged after 30 days, billing records are retained as required by law.
Every account is strictly scoped so your data is only ever visible to you.
Built and hardened by GRC consultants, not bolted on after the fact.
A 15-question scored assessment across CAF, ISO 27001, Cyber Essentials and Cyber Insurance. Answer honestly, see exactly where your real gaps are, in about five minutes.
Take the Free Check →
A downloadable guide to how UK SMEs actually get certification, insurance and tender-ready, what auditors ask for, and the most common gaps we see before a first assessment.
Get the Free Guide →
CAF · ISO 27001 · Cyber Insurance
See the full pack →
The Lower-Cost Baseline
See Cyber Essentials / CE+ →
Whether it's public sector procurement, an enterprise vendor assessment, or your cyber insurance renewal, start with the package that matches what's actually being asked of you.
A fully customised, audit-ready framework containing your full set of security policies and procedures aligned to your chosen package, plus a Targeted Improvement Plan (TIP) and automated tools to keep your policies up to date. See the full toolkit for everything included.
No. We are pure Governance, Risk, and Compliance documentation specialists. We provide the procedural frameworks, policy rules, and implementation roadmaps, your internal team or outsourced MSP handles the technical engineering.
A first draft of your documents is available in your portal as soon as you sign up, built from whatever you've answered so far. Reaching a genuinely complete, audit-ready state means working through the rest of your package's guided questions, each document updates automatically as you go.
Absolutely not. Your corporate answers are processed entirely in-memory using an isolated engine running inside our secure private UK-hosted server. Your data never touches public cloud AI networks and is never used for training public models.
Static security policies erode quickly as your business changes, rendering them useless to insurers and auditors. Your subscription includes a Narrative Check in your portal where you can flag anything that's changed each quarter, automated affected-document flagging whenever an answer changes, and review-reminder emails, keeping your documentation aligned with your real-world setup.
The latest guidance and reporting from the UK National Cyber Security Centre, the body whose Cyber Assessment Framework underpins CAF certification.
Couldn't load the latest NCSC updates right now, check back shortly.
Content and headlines from ncsc.gov.uk. CyberSec Compliance is not affiliated with or endorsed by the NCSC.